Français
 DE

In an increasingly connected industrial environment, data security, service availability and control over information systems have become major priorities.
After several months of work, NEXESS has successfully completed its SOC 2® Type 2 examination, performed by the independent auditor Sensiba LLP.
Initially launched with a focus on the Security criterion, the project ultimately resulted in a report covering three Trust Services Criteria:
- Security
- Availability
- Confidentiality
The report covers the NEXESS Software as a Service System for the period from June 19 to September 18, 2026.
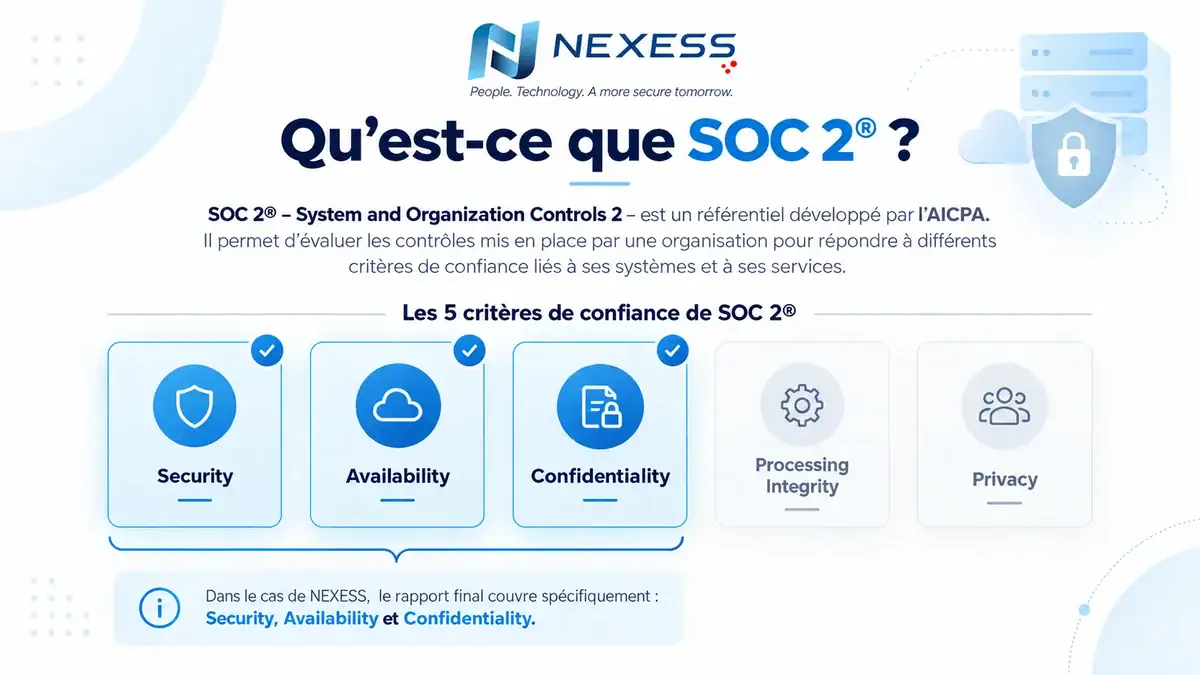
The 5 SOC 2 Trust Services Criteria and the scope covered by the NEXESS report.
What is SOC 2®?
SOC 2® (System and Organization Controls 2) is a framework developed by the AICPA (American Institute of Certified Public Accountants).
It is used to evaluate the controls an organization has implemented to meet various trust criteria related to its systems and services.
Depending on the agreed scope, a SOC 2 examination can cover five categories: Security, Availability, Processing Integrity, Confidentiality and Privacy.
For NEXESS, the final report specifically covers Security, Availability and Confidentiality.
A workspace dedicated to compliance monitoring and access control, as part of the SOC 2 Type 2 audit.
SOC 2 Type 1 vs. Type 2: what is the difference?
A SOC 2 Type 1 report looks at the design of controls at a specific point in time.
SOC 2 Type 2 goes further: it assesses both the design of controls and how effectively they operate over a defined period.
For NEXESS, the examination covered the period from June 19 to September 18, 2026. Sensiba evaluated the design and operating effectiveness of the controls associated with the selected criteria.
A broader scope than initially planned
When the project started, the main objective was to structure the approach around the Security criterion.
As the project progressed, NEXESS was able to go further and add two more criteria to the final scope: Availability and Confidentiality.
This reflects the work done in just a few months to structure processes, formalize controls and strengthen the internal practices required for SOC 2.
The report therefore covers:
- Security: protecting information and systems against unauthorized access and risks that could affect their availability or confidentiality.
- Availability: the ability of systems and information to remain available in line with defined objectives.
- Confidentiality: protecting information designated as confidential.
What SOC 2 Type 2 means for NEXESS customers
NEXESS solutions rely on connected equipment, traceability technologies and software platforms that collect and use data from industrial operations.
In this context, system security and reliability are inseparable from the performance of our solutions.
Completing the SOC 2 Type 2 examination gives NEXESS customers and partners an additional basis for trust, grounded in an independent assessment of the controls associated with the company’s SaaS system.
The report describes measures related to access management, system monitoring, incident management, backups, business continuity and risk management.
Real-time monitoring of a connected industrial infrastructure, one of the key controls assessed during the audit.
Beyond the audit: a lasting change in practices
SOC 2 Type 2 is not just the outcome of an audit.
The project has also changed the way NEXESS approaches security, traceability, risk management and continuous improvement.
Controls must continue to be applied, monitored and adapted over time. The report itself stresses the importance of ongoing monitoring and improvement of internal controls.
SOC 2 is therefore a long-term commitment: maintaining the practices put in place, developing them and continuing to strengthen the trust we offer our customers and partners.
Team meeting dedicated to process monitoring and the continuous improvement of security practices.
A new milestone for NEXESS
With the completion of its SOC 2® Type 2 examination, NEXESS reaches a new milestone in delivering reliable and secure industrial digital services.
Beyond the audit result, this approach reflects a clear commitment: to keep structuring our practices and to build lasting trust in our solutions.
Discover the NEXCAP® software platform and read our Privacy Notice.
People. Technology. A more secure tomorrow.
Want to learn more about our compliance and security approach?
Contact usFAQ
No. SOC 2 is an attestation report issued following an independent examination. Sensiba actually recommends not using the term “SOC 2 certification”.
The report covers three Trust Services Criteria: Security, Availability and Confidentiality.
The report covers the NEXESS Software as a Service System for the period from June 19 to September 18, 2026.
The full report contains confidential information and is not intended for public release. It can be shared with relevant parties in an appropriate framework, in particular under a non-disclosure agreement. A status letter can also officially confirm that the report has been issued without disclosing its detailed content.
Related articles
Revolutionizing Tool Calibration Management with RFID-Based Solutions
In today’s fast-paced industrial landscape, the need for efficient and precise tool calibration management has...
READ MOREJan